Secure push-to-talk you can run on premise.
Respondr is built for operators who have to prove how their communications work, not just describe them. Encrypted transport, identity you already run, permissions per channel, and a record behind every action.

Your data stays where you decide.
Free, Essential and Business run on Respondr Cloud, hosted by AWS in the European Union. With Enterprise the server is dedicated: you can keep it in your own network or on AWS in the country you choose, and connect your radios through gateways on site.

Identity you already run, permissions per resource.
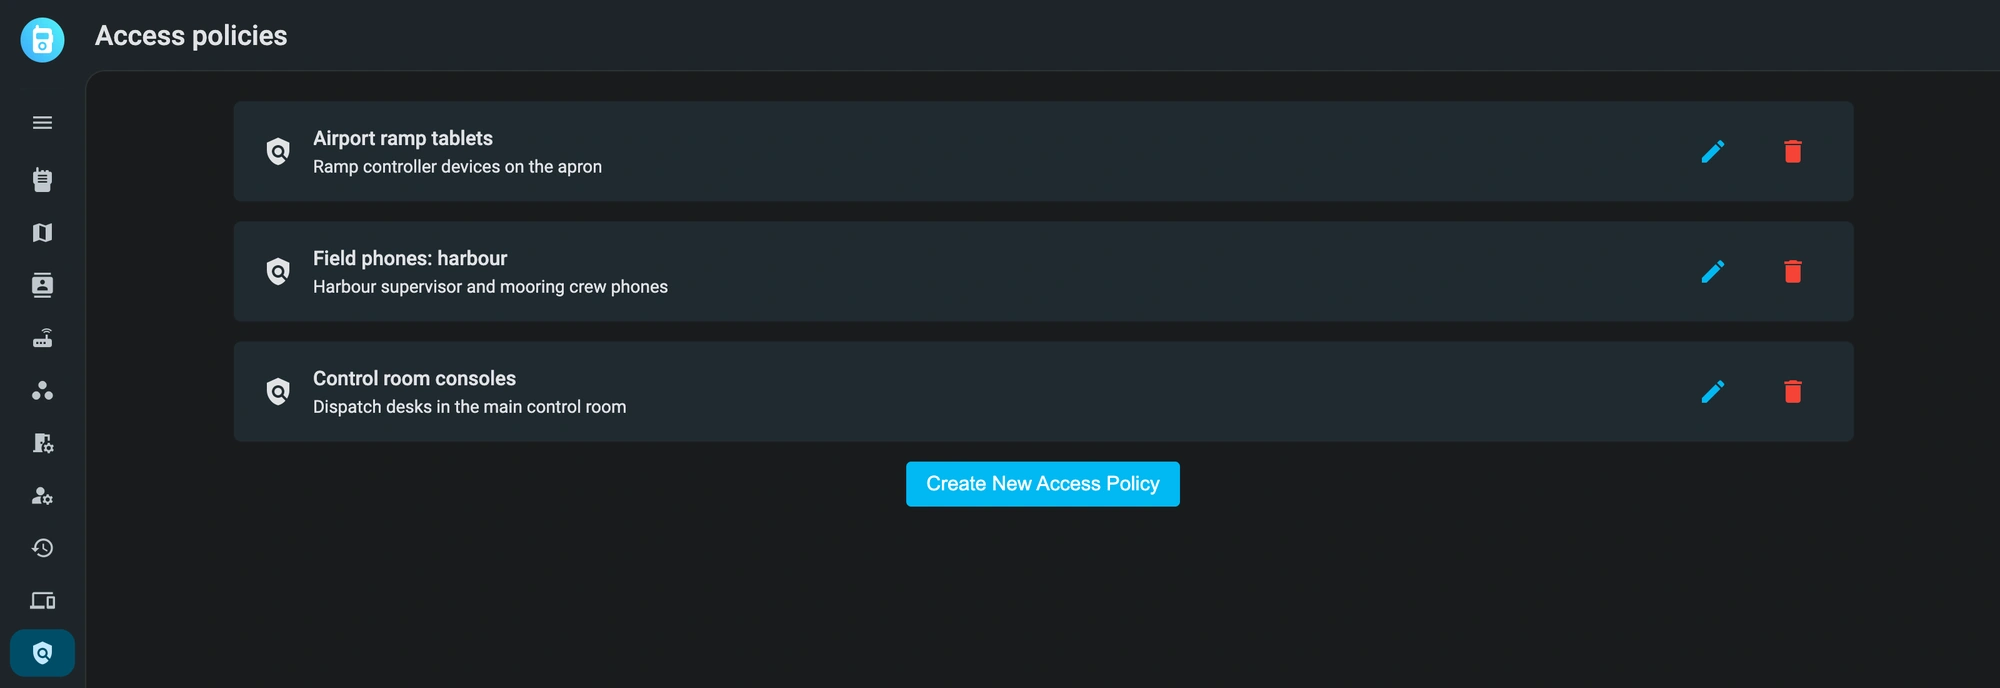
Users sign in through your corporate identity provider over OIDC, with TOTP multi-factor on the accounts that need it. Access is then granted per resource — which channels a person can hear, which gateways they can touch, which settings they can change.
Every transmission leaves a record.
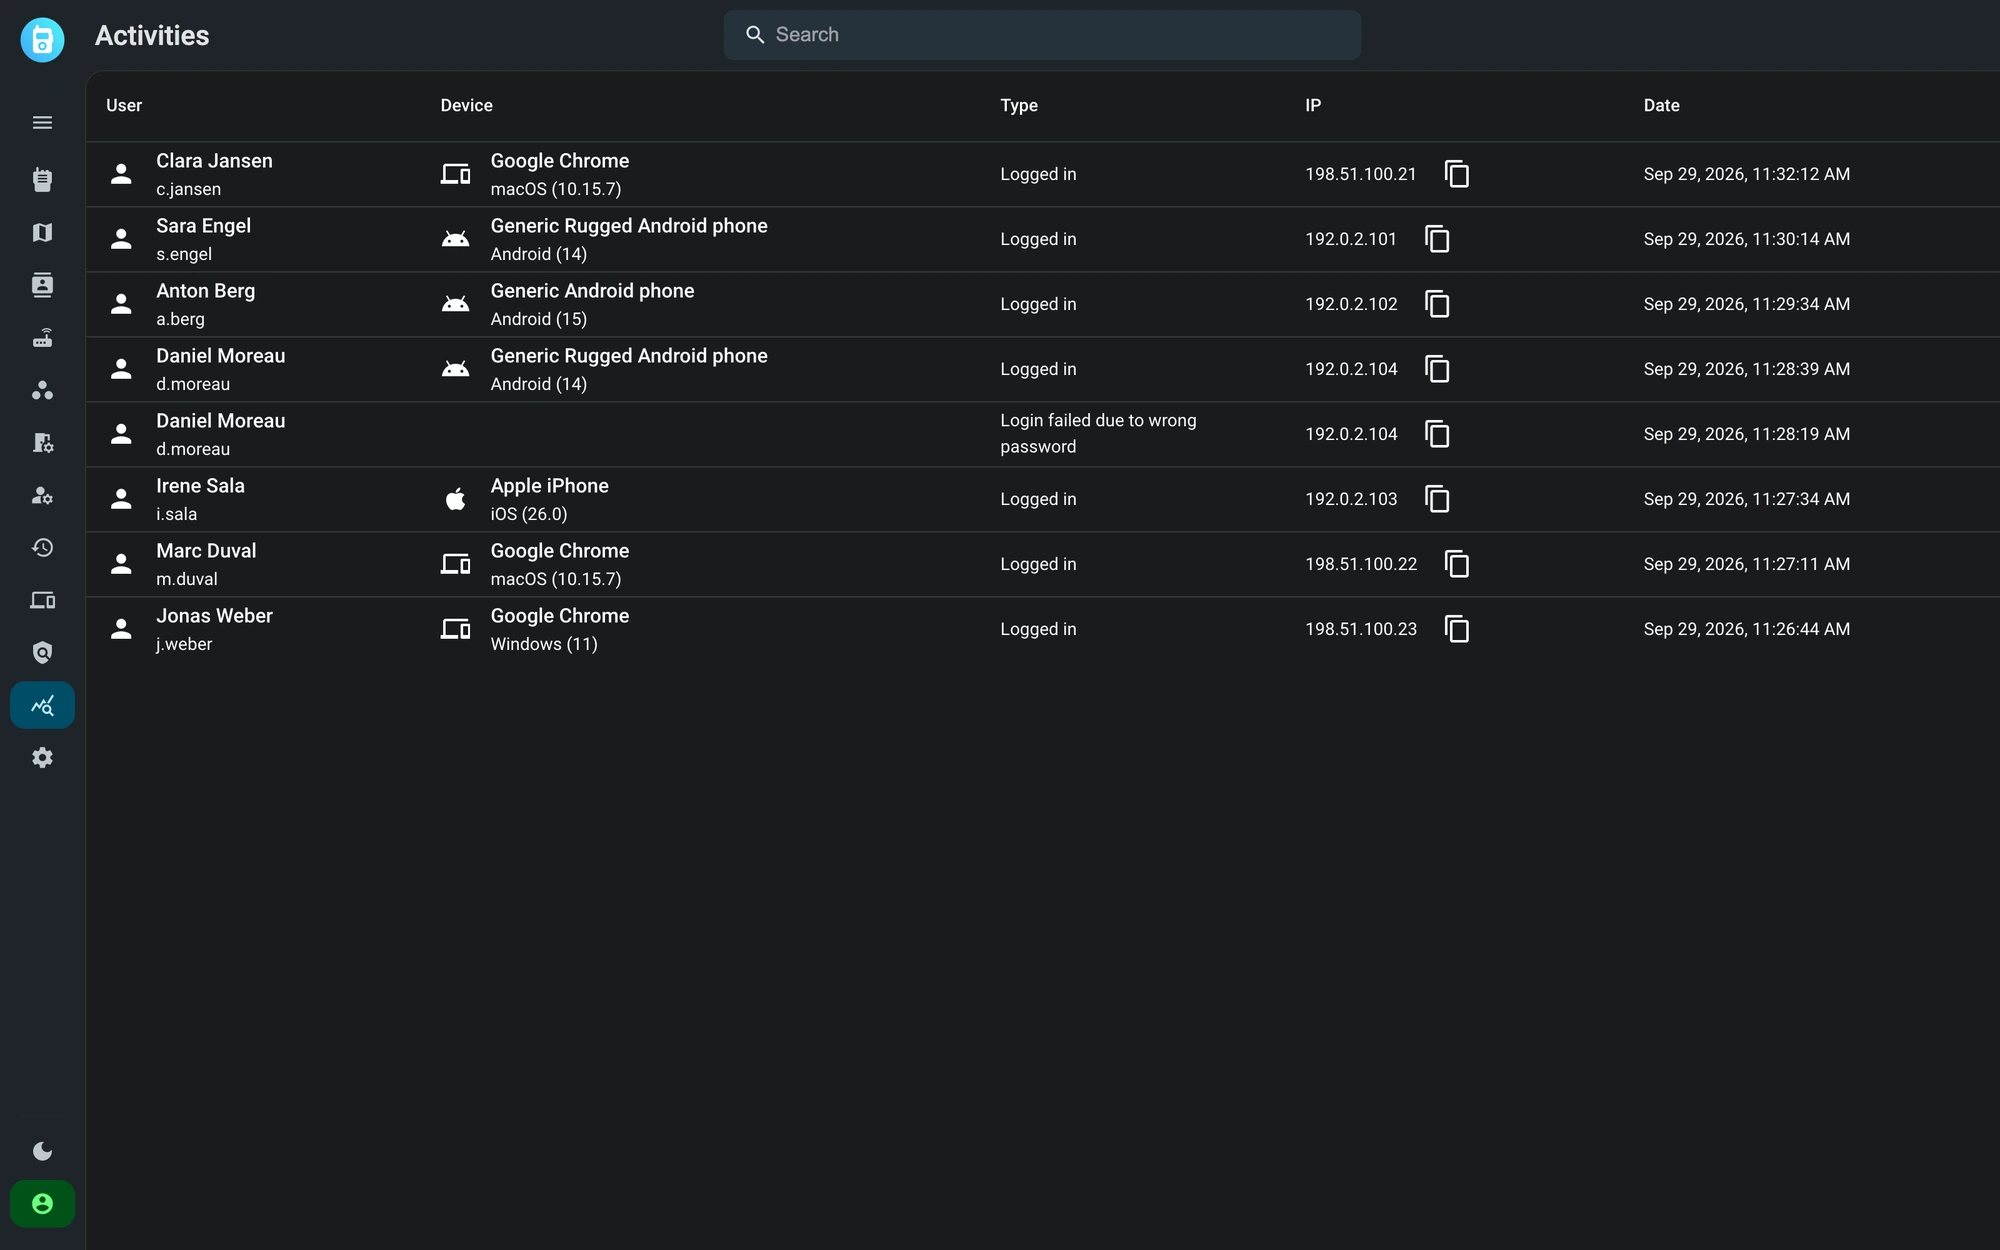
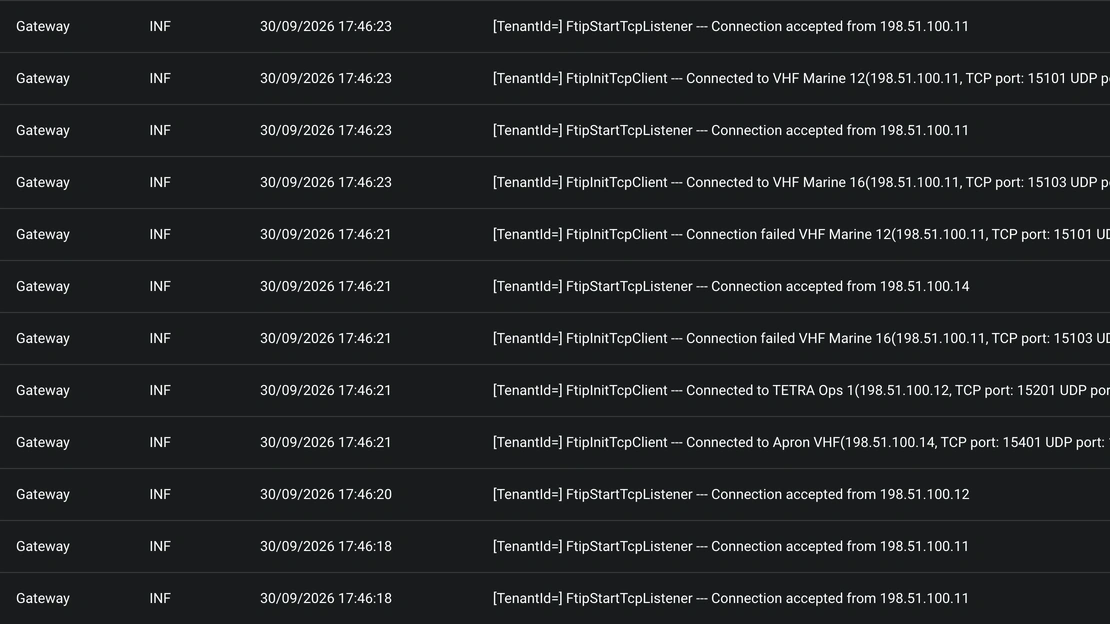
With Business and Enterprise, channel audio is recorded and searchable, and on every plan the platform keeps separate logs for application events, gateway communication and the real-time hub. When a review asks what was said and who did what, the answer is a query, not a reconstruction.
The controls, one by one
What is enforced by the platform rather than by policy. These are the mechanisms a security questionnaire asks about.
Encrypted voice and messages
Multi-factor authentication
Account lockout
OIDC single sign-on
Per-resource permissions
Audit logging
Where your data lives
| Deployment | Storage and encryption |
|---|---|
| Respondr Cloud | Free, Essential and Business. AWS Europe region, encrypted volumes. |
| Enterprise on premise | Your hardware, inside your network. Disks encrypted with LUKS / dm-crypt. |
| Enterprise on AWS | A dedicated instance in the AWS region of the country you choose. Volumes encrypted with EBS and KMS. |
| In transit | TLS 1.3 between the app, the console and the server; AES-128-GCM on audio sent over UDP. |
| At rest | Recordings and saved messages encrypted with AES-256. |
Standards and frameworks
Where Respondr sits against the frameworks European operators are assessed on. None of these is a product certificate issued by a third party; the NIS2 and IEC 62443 page explains what each one means for Respondr.
IEC 62443
NIS2
GDPR data residency
Operational continuity
Frequently asked questions
No. Respondr holds no IEC 62443 certification from a third-party body. The architecture is designed with reference to the standard, targeting Security Level 2, and NIS2 certifies no products: Respondr helps you meet its obligations. We can walk your security team through which controls answer which requirement.
Yes, with the Enterprise plan. The complete stack, core, database and recording, runs on your own hardware inside your network. Local radio gateways keep working with no external connection at all.
With Free, Essential and Business it is hosted by AWS in the European Union, on encrypted volumes. With Enterprise the server is dedicated: on premise the data never leaves your building, and on AWS it stays in the country you choose, on volumes encrypted with EBS and KMS.
Yes, with Business and Enterprise. Respondr connects to external identity providers over OIDC, configured per organization, so accounts are created and removed where you already manage them.
No. Application, gateway and hub logs each have their own retention window, and recording retention is a deployment setting. Keeping everything indefinitely is a liability, not a feature.
Consumer PTT services are hosted for you, in a region they choose, with one account model. Respondr can run entirely inside your infrastructure, authenticates against your identity provider, grants access per channel, and logs what happened.
We’ll show you Respondr in a live demo.
We offer a 30-minute live demo built around your radio infrastructure.